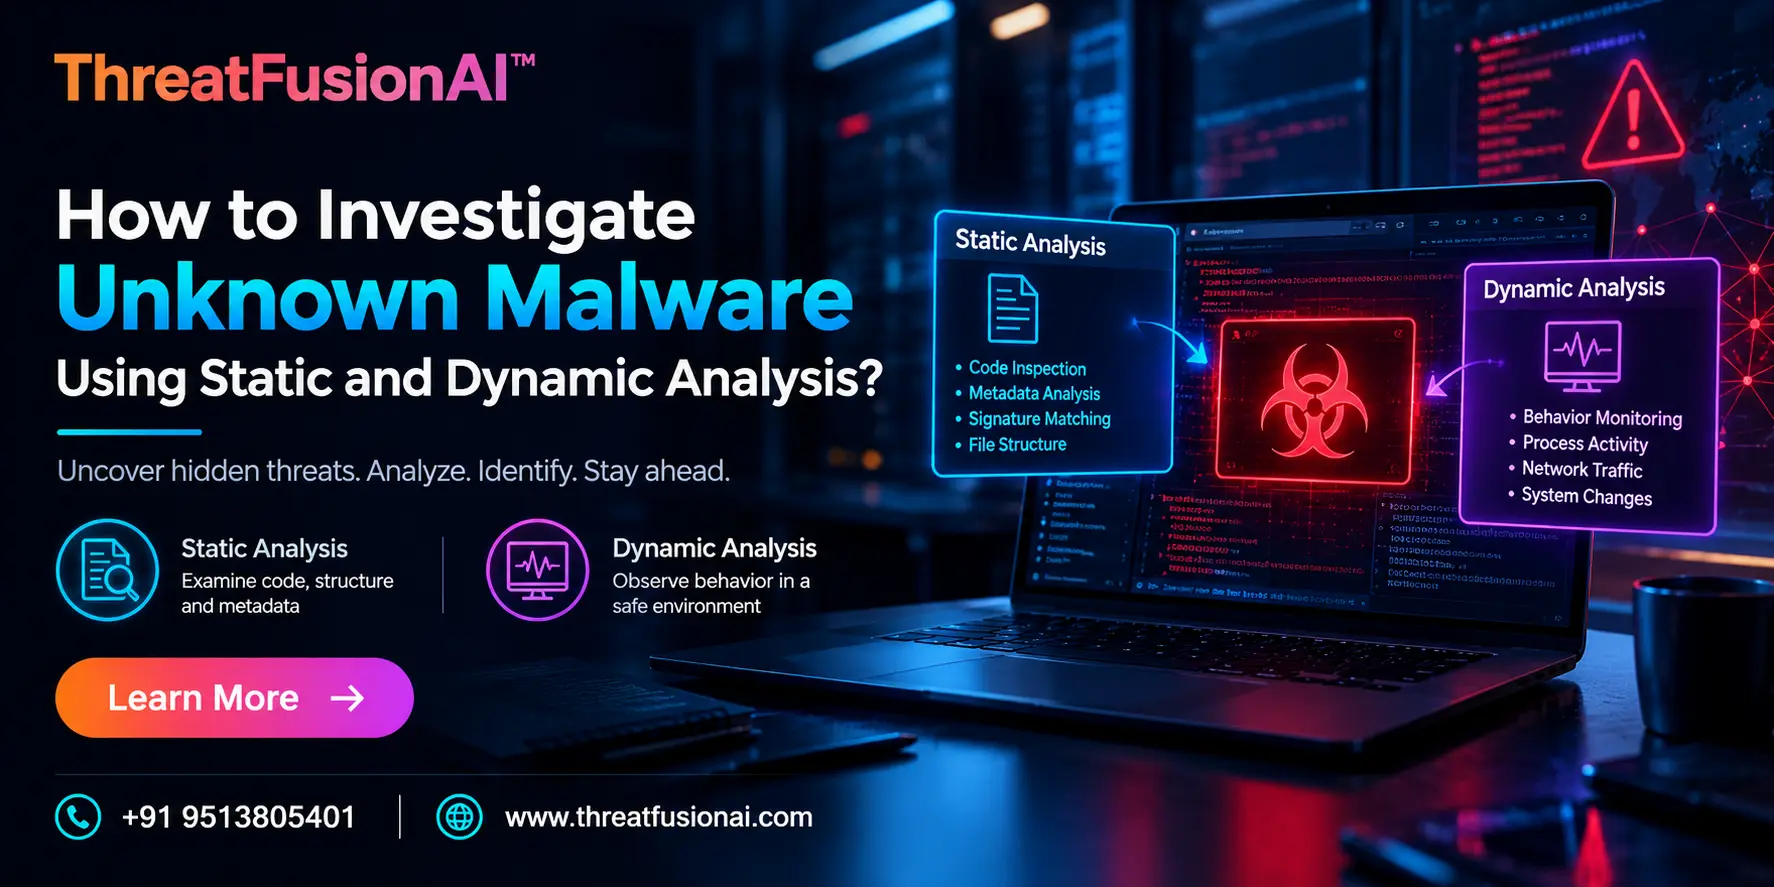
Do you know the differences between Static and Dynamic Malware Analysis and their benefits for organizations in the IT Industry? If not, then you are in the right place. Here, we will talk about what these analysis methods are and related benefits in detail.
Moreover, we will introduce you to a reliable threat intel solution offered by a reputable VAPT service provider. What are we waiting for? Let’s get straight to the topic!
What Is Malware Analysis?
The process of breaking down dangerous software, such as viruses, ransomware, and spyware, to comprehend its behavior, source, and possible effects is known as malware analysis. Security analysts watch how the code runs, interacts with external servers, and gets around defenses by isolating it in a sandbox.
By producing actionable threat intelligence, this process helps enterprises improve network security and create focused remediation plans. Let’s explore the difference between Static and Dynamic Malware Analysis in detail!
Why Is Malware Analysis Important?
Malware analysis is important for the following reasons:
1. Accelerates Incident Response & Containment: Allows for quick triage and isolation of compromised computers by promptly identifying the extent and capabilities of the infection.
2. Uncovers Indicators of Compromise (IoCs): Extracts registry keys, file hashes, and network signatures to search systems throughout the company for hidden infections.
3. Strengthens Defensive Controls: Enables proactive blocking of similar threat variants before re-entry by providing information to firewalls, endpoint protection (EDR), and detection rules.
4. Provides Actionable Threat Intelligence: Tracks actor profiles and predicts upcoming assault campaigns by decoding opponent tactics, methods, and procedures (TTPs).
5. Mitigates Financial & Operational Impact: Quickly eliminates active security threats to avoid expensive downtime, data exfiltration, and reputational harm.
What Is the Difference Between Static and Dynamic Malware Analysis?
|
S.No. |
Topics |
Factors |
What? |
|
1. |
Static Malware Analysis |
Execution State |
Removes the possibility of system infection during evaluation by examining the binary code, headers, strings, and metadata without actually running the file. |
|
Primary Objective |
It extracts signature-based artifacts to determine intent and spot known dangers, including cryptographic hashes, imported libraries, and embedded URLs. |
||
|
2. |
Dynamic Malware Analysis |
Execution State |
Observes the suspicious file's live behavior in real time by running it in a separate sandbox or virtual environment. |
|
Primary Objective |
Analyzes complex, obfuscated, or unknown malware strains by capturing runtime behaviors like as process spawning, registry changes, API requests, and outgoing command-and-control (C2) network traffic. |
How to Set Up a Safe Malware Analysis Environment?
You can set up a safe malware analysis environment in the following ways:
● Isolate via Dedicated Virtualization Software: Execute guest targets within hypervisors such as VMware Workstation or VirtualBox.
● Configure Host-Only or Isolated Virtual Networking: Use internal virtual networks or special host-only adapters to route visitor traffic.
● Disable Host-Guest Integration Features: Disable shared memory drivers, drag-and-drop, shared files, and clipboard sharing.
● Establish Baseline Snapshots Before Analysis: After running malicious files, quickly undo changes by capturing a clean virtual machine state.
● Implement Dynamic Analysis Defenses: To evade anti-analysis procedures, alter registry keys, MAC addresses, and system specifications.
How to Perform Automated Malware Triage and Hash Lookup?
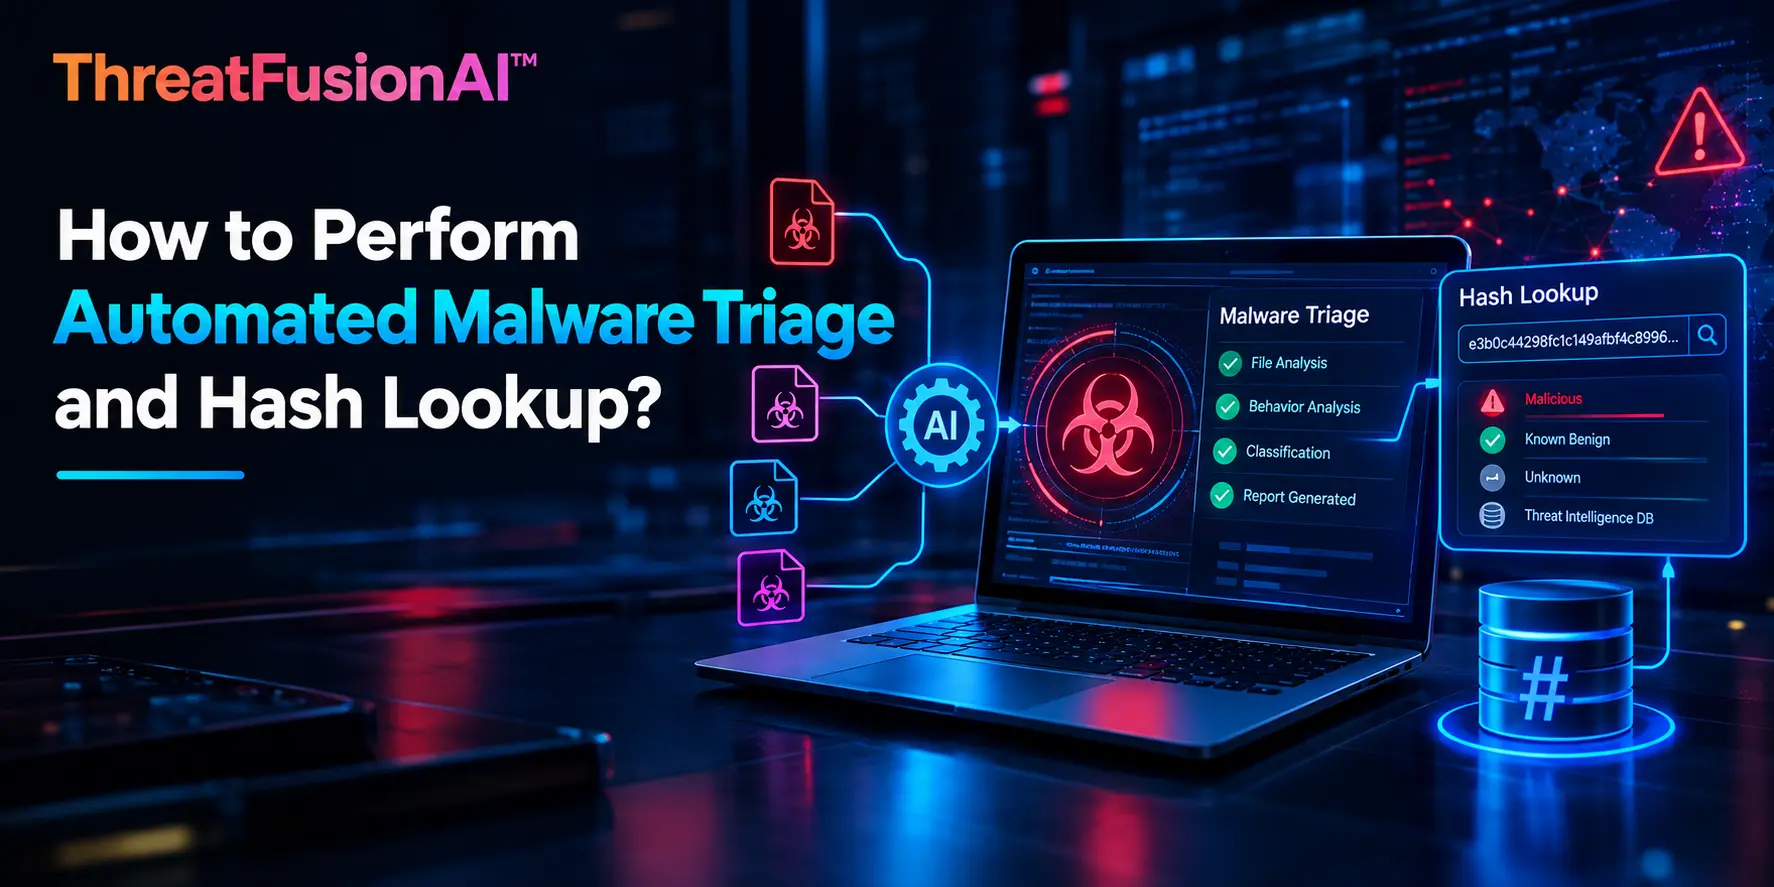
You can perform automated malware triage and hash lookup in the following ways:
a) Generate Unique Cryptographic Fingerprints: Utilizing local command-line tools, determine the suspicious file's MD5, SHA-256, and SSDEEP hashes.
b) Query Automated Threat Intelligence APIs: To verify past detection rates, send hashes via automated scripts to sites such as VirusTotal or Hybrid Analysis.
c) Extract Known Indicators of Compromise (IoCs): Obtain threat metadata, such as known malicious file names, C2 IP addresses, and related malware families.
d) Apply Severity Scoring & Routing Rules: Prioritize high-threat samples for manual analyst assessment by automatically classifying files based on risk scores.
e) Enrich SIEM and EDR Detection Pipelines: To start global blocking, push verified threat hashes and indicators straight into endpoint and network security systems.
How to Investigate Unknown Malware Using Static Analysis?
|
S.No. |
Factors |
How? |
|
1. |
Determine File Type and Format Architecture |
Use a file to identify or detect magic bytes. PE, ELF, or Mach-O structures are simple to verify. |
|
2. |
Extract Embedded Human-Readable Strings |
To extract registry paths, IP addresses, hardcoded URLs, and plain text, use strings or Floss. |
|
3. |
Inspect Imported and Exported API Functions |
Use CFF Explorer to examine the Import Address Table (IAT) and map network and system capabilities. |
|
4. |
Analyze Executable Headers and Section Entropy |
To identify obfuscation and hidden payloads, use PEview to measure section packing and randomness. |
|
5. |
Disassemble Code via Reverse Engineering |
To examine the underlying assembly instructions and control flow, load the binary into Ghidra or IDA Pro. |
Best Tools for Static and Dynamic Malware Analysis
The following are the best tools for static and dynamic malware analysis:
1. Ghidra & IDA Pro: To examine the underlying assembly code and logic flow, decompile and deconstruct built binaries.
2. PeStudio & PE-bear: For quick initial triage, examine section entropy, metadata, and Portable Executable (PE) headers.
3. ANY.RUN & CAPE Sandbox: Set off samples in interactive or automated sandboxes to record C2 traffic and real-time behavioral records.
4. x64dbg & WinDbg: To step through instructions, get around anti-analysis checks, and unpack payloads, debug live binaries at runtime.
5. Wireshark & Process Monitor: Record unprocessed network data and keep an eye on changes to the file system, registry, and processes in real time.
How to Analyze Unknown Malware Using Dynamic Analysis?
You can analyze unknown malware using dynamic analysis in the following ways:
● Establish System and Baseline Snapshots: Record memory dumps, file and registry baselines, and the system state before execution.
● Simulate Network Infrastructure: To intercept outgoing C2 requests, launch phony internet services such as INetSim or FakeDNS.
● Execute Sample and Trigger Behavioral Vectors: Use administrator credentials to run the malware sample, responding to requests to activate hidden payloads.
● Monitor Memory, Process Trees, and Network Artifacts: Use Wireshark and Process Monitor to monitor file changes, network connections, and process injection.
● Compare Post-Execution Diff and Revert VM: Create system diff logs to record modifications, and then clean up the virtual machine snapshot.
How to Conduct Memory Analysis and Volatile Artifact Extraction?
|
S.No. |
Factors |
How? |
|
1. |
Dump Volatile RAM |
Before shutting down, use tools like FTK Imager, WinPmem, or LiME to capture physical memory in order to retain its volatile state. |
|
2. |
Identify OS Profile & Context |
To guarantee proper symbol alignment, use Volatility or Rekall to determine the kernel architecture and OS build. |
|
3. |
Extract Active & Hidden Processes |
To identify unlinked, concealed, or injected jobs, enumerate process trees and cross-reference structures (pslist, psxview). |
|
4. |
Recover Network Connections & Handles |
Look for open file handles, listening ports, and active sockets in memory structures (netscan, handles). |
|
5. |
Carve Executable Payloads & Injection |
For offline static inspection (malfind, procdump), extract DLLs, unhooked binaries, and inserted code segments straight from RAM. |
Common Challenges in Static and Dynamic Malware Analysis
The following are the common challenges faced in static and dynamic malware analysis:
a) Advanced Obfuscation and Packing: Malicious strings are concealed and static disassemblers are blinded by encrypted payloads, specialized packers, and code polymorphism.
b) Anti-Analysis and Environment Awareness: In order to avoid dynamic monitoring, anti-debugging, VM fingerprinting, and sandbox checks cause execution halts.
c) Time-Delayed and Conditional Execution: Time-limited sandbox runs are circumvented by extended sleep cycles, reboot triggers, and particular geographic or user-interaction requirements.
d) Fileless Malware and Memory-Only Execution: Direct RAM injection and living-off-the-land methods (LOLBins) create no disk artifacts for static analysis.
e) Evolving C2 Infrastructure and Encrypted Protocols: Real-time network traffic analysis is obscured by peer-to-peer C2 channels, SSL/TLS decryption hurdles, and domain generation algorithms (DGA).
How to Detect Anti-Analysis, Anti-Debugging, and Evasion Tactics?
You can detect anti-analysis, anti-debugging, and evasion tactics in the following ways:
1. Inspect Anti-Debugging API Calls: Examine import tables and follow calls to functions such as CheckRemoteDebuggerPresent and IsDebuggerPresent.
2. Check Environment Registers and Flags: Check for set BeingDebugged and NtGlobalFlag values in readings from the Process Environment Block (PEB).
3. Identify Timing Checks and Delays: Use GetTickCount or RDTSC to identify instruction pairings that are intended to quantify the execution latency between instructions.
4. Detect Hardware Breakpoints and Exception Handlers: Audit GetThreadContext calls for custom structured exception handlers (SEH) and active debug registers (DR0–DR7).
5. Audit Sandbox & VM Artifact Probes: Keep track of queries looking for low system resource profiles, display drivers, registry strings, and hypervisor MAC addresses.
When to Transition from Static and Dynamic Analysis to Reverse Engineering?
When automated sandboxes and basic inspection fail because of extensive packing, code obfuscation, or bespoke encryption, go from static and dynamic analysis to reverse engineering. When you need to extract embedded cryptographic keys, recreate proprietary command-and-control protocols, or demonstrate the precise operating logic of an unidentified zero-day payload, it becomes crucial.
How to Identify Malware Indicators of Compromise (IOCs)?
You can identify malware IOCs in the following ways:
● Analyze Network Traffic and DNS Artifacts: Examine PCAP files to record user-agent strings, suspicious domain requests, and outgoing C2 IP addresses.
● Extract File System and Cryptographic Signatures: Determine the MD5 and SHA-256 file hashes and note any newly generated, renamed, or altered system paths.
● Inspect Memory and Volatile Artifacts: Examine RAM dumps for loaded DLL base addresses, injected code segments, and unlinked processes.
● Audit API Hooking and Process Trees: Monitor instances of unlawful privilege escalation, API function overwrites, and strange parent-child process interactions.
● Harvest Static Code and String Metadata: Directly extract mutex names, embedded configuration URLs, internal debug routes, and hardcoded cryptographic keys from programs.
How to Document Findings and Write an Actionable Malware Analysis Report?
You can document findings and write an actionable malware analysis report in the following ways:
● Executive Summary & Metadata: For non-technical stakeholders, summarize the main conclusions, risk level, threat attribution, and file metadata.
● Technical Analysis & Execution Timeline: Give a chronological account of the infection chain, network activity, process behavior, and memory artifacts.
● Extracted Indicators of Compromise (IoCs): Enumerate every file hash, domain name, C2 IP address, registry path, and attack signature that has been confirmed.
● Detection & Mitigation Controls: To contain and stop the threat, provide actionable defense rules, SIEM queries, and corrective actions.
● YARA & Appendices (Raw Artifacts): Add PCAP captures, dynamic analysis logs, decompiled code snippets, and custom YARA rules.
Conclusion: How to Investigate Unknown Malware Effectively?
Now that we have talked about what Static and Dynamic Malware Analysis are, you might want to get your hands on a dedicated threat intel solution from a reliable source. For that, you can go for ThreatFusionAI, a dedicated threat intel platform offered by Craw Security.
ThreatFusionAI can help businesses by notifying them about the latest cyber threats and malicious risks so that they can improve their security measures for future threats. What are you waiting for? Contact, Now!
Frequently Asked Questions
About Static and Dynamic Malware Analysis
1. What Is Static Malware Analysis?
By examining an executable's code, structure, and metadata without actually running it, static malware analysis enables researchers to safely extract signs of compromise without running the risk of infecting a system.
2. What Is Dynamic Malware Analysis?
The technique of running a suspicious file in a secure environment, like a sandbox or virtual machine, to watch and document its live runtime behavior, process activity, and network connectivity is known as dynamic malware analysis.
3. What Is the Difference Between Static and Dynamic Malware Analysis?
While dynamic analysis runs the malware in an isolated sandbox to see its live activity and network traffic, static analysis looks at code, metadata, and binary structure without running the file.
4. How Do You Investigate Unknown Malware Safely?
You can investigate unknown malware safely in the following ways:
a) Perform Static Analysis First in an Isolated Environment,
b) Isolate the Virtual Machine via Host-Only Networking,
c) Simulate External Services with Air-Gapped Tools,
d) Establish and Revert Baseline Snapshots, and
e) Enforce Sandbox Hardening and Anti-Evasion Defenses.
5. What Are the Best Tools for Malware Analysis?
The following are the best tools for malware analysis:
a) Ghidra & IDA Pro,
b) PeStudio & PE-bear,
c) ANY.RUN & CAPE Sandbox,
d) x64dbg & WinDbg, and
e) Wireshark & Process Monitor.
6. Can Static Analysis Detect Malware Without Executing It?
Yes, by comparing known threat signatures and heuristics to file structures, embedded text, hashes, headers, and code patterns, static analysis finds malware without requiring execution.
7. Why Is a Sandbox Important for Dynamic Malware Analysis?
A sandbox is important for dynamic malware analysis for the following reasons:
a) Infection Containment & Isolation,
b) Real-Time Behavioral Observation,
c) Outbound Network Traffic Inspection,
d) Bypassing Code Obfuscation & Packers, and
e) Automated Evidence & IOC Generation.
8. How Do You Identify Indicators of Compromise (IOCs) in Malware?
You can identify IOCs in malware in the following ways:
a) Analyze Outbound Network Connections & DNS Requests,
b) Extract File System Signatures & Hashes,
c) Carve Volatile RAM Artifacts,
d) Audit API Hooking & Process Lineage, and
e) Harvest Embedded Strings & Mutexes.
9. What Are the Common Challenges in Malware Analysis?
The following are the common challenges in malware analysis:
a) Advanced Obfuscation and Packing,
b) Anti-Analysis and Environment Awareness,
c) Time-Delayed and Conditional Execution,
d) Fileless Malware and Memory-Only Execution, and
e) Evolving C2 Infrastructure and Encrypted Protocols.
10. How Can Static and Dynamic Analysis Be Combined to Detect Unknown Malware?
Static and dynamic analysis can be combined to detect unknown malware in the following ways:
a) Initial Static Triage to Establish Hashes and Attributes,
b) Instrumented Dynamic Execution in an Isolated Sandbox,
c) Memory Forensics Driven by Runtime Triggers,
d) Iterative Reverse Engineering of Dynamic Obfuscation, and
e) Cross-Correlating Static and Dynamic Artifacts for Complete IOC Mapping.